Your performance review (smishing!)

This example is not another phishing email. Instead, it is a smishing attack, where criminals use SMS text messages to deliver their lure.

The message claims to come from “UVic HR” and states that a performance review is ready for viewing. The sender attempts to add legitimacy by using the university’s name and a routine HR topic that may be relevant to many employees. Recipients are then directed to click a shortened URL to access the alleged review.

There are several signs that this message is not legitimate:

  • The text originates from an unknown phone number, not an official UVic communication channel.
  • The sender uses a shortened URL, making it impossible to determine the actual destination before clicking.
  • The message includes the recipient’s name, but don’t let that fool you. Attackers frequently personalize their messages using information obtained from public sources or previous data breaches. A personal greeting is not proof that a message is legitimate.
  • Performance reviews and other HR-related information would be accessed through established university systems, not through links delivered by unsolicited text messages.

One notable aspect of this attack is that it attempts to move the interaction outside of UVic’s email environment. Security controls, phish filtering, and reporting mechanisms are most effective when communications remain within university-managed systems. By contacting recipients directly through SMS, attackers hope to avoid those protections and create a greater sense of trust and urgency.

Like phishing emails, smishing messages often rely on curiosity, urgency, or fear to encourage quick action. Taking a moment to pause and think critically is often all it takes to avoid becoming a victim.

Do not click suspicious links, do not reply to unexpected text messages, and do not provide personal information or credentials. Stay vigilant and think before you click.


Here is the transcript of the message:
From: +1 (855) 699-<redacted>
Uvic HR: Dear <your name>!
Your performance review is ready for viewing:
https://kla4.io/<redacted>

Annual Conflict of Interest Check-In

This phish was received by many UVic recipients. It impersonates the University of Victoria Human Resources department.

The message attempts to create a sense of urgency by asking recipients to complete an “Annual Conflict of Interest Check-In” through a purported HR portal. Recipients are encouraged to click a button labeled “Go to HR portal”, which is designed to direct users to a fraudulent website with the goal of stealing your UVic credentials.

Several indicators reveal that this message is not a legitimate university communication:

  • External Sender – The email claims to be from the University of Victoria (display name – “University of victoria”), but it comes from a non-UVic domain.
  • No Subject Line
  • Threat actors frequently use topics that appear routine and administrative because they are less likely to raise suspicion.
  • Pressure to Act – encourages recipients to complete the task “this week” and notes that responses are needed from every team member. Creating urgency is a common phishing tactic designed to reduce careful scrutiny.
  • Suspicious Link – The email contains a button labeled “Go to HR portal”. In fact it points to an external web site.

As always, please resist the temptation to click suspicious links. Malicious websites may contain payloads that can compromise your device. If you receive a suspicious email, report it instead. Our Information Security team investigates these sites safely in a secure lab environment.

The transcript of the body of the message follows for your information.


UNIVERSITY OF VICTORIA HR
Annual Conflict of Interest Check-In
Hi , <redacted>
It’s that time of year again for our quick Code of Conduct and Conflict of Interest check-in. I know these forms can feel like routine paperwork, but we ask everyone to complete one—even if you have nothing new to report! Here are the quick steps:

Hit submit—no attachments or signatures required.
Go to HR portal
Could you please take a quick moment to wrap this up sometime this week? It usually takes less than two minutes, and because we need a response from every team member, your submission really helps us stay on track.
If you have any questions at all, feel free to reply directly to this email—I’m happy to help.
Thanks so much for your time,
HR at University of victoria

Log into the HR portal and open the “Conflict of Interest” form.

Review the brief questions—if nothing applies to you, simply select “nothing to report.”

Salary Increase Announcement

A targeted phishing email claiming that all UVic staff are receiving a 20% salary increase to trick you into opening a phishing PDF

A 20% salary increase sounds tantalizing, doesn’t it? That’s why phishers love to use that theme, especially nowadays when the cost of living is so high. But as the old saying goes, if it sounds too good to be true, it probably is, and that certainly applies to this phishing email.

The other key sign that this email is not legitimate is the fact that it came from outside of UVic. Official university communications, especially HR and payroll related items, would all come from UVic email addresses.

Finally, accessing your salary information would not require clicking a link or button in a password-protected PDF attachment in order to login. If a PDF tells you to click on a link to access “secure” or “protected” content, that is a very strong sign of a phish, even more so if it also tells you to create MFA bypass codes like we saw in a similar phish from March. When in doubt, login to www.uvic.ca like you normally would and use the links on the Online Tools page to get where you need to go.

From: Payroll <[redacted non-UVic sender]>
Subject: Salary Increase Announcement

Attachment: [PDF icon] University_of_Victoria_Comp… 295 KB

You don’t often get email from [redacted]. Learn why this is important

Dear Staff,

On behalf of the Human Resources Department at the University of Victoria, we are pleased to share an important update.

In recognition of your continued hard work, dedication, and the success you contribute to our institution, the University will be implementing a 20% salary increase for all staff. This decision reflects our deep appreciation for your commitment to excellence and the vital role you play in supporting our academic community.

Note: Your αccess is required to review the officiαl sαlαry increment letter.
Initiαl αccess code: Salary2026

Your efforts, professionalism, and dedication have been instrumental in advancing the University’s mission and strengthening our community. We are grateful for your contributions and proud to have such a committed team.

Thank you for your ongoing hard work and dedication. We look forward to continuing our success together.

Sincerely,
Human Resources Department
University of Victoria

Message From University Of VictoriaHR Portal

As you can tell, scammers continue to explore this theme. The new phishing email that arrived today – and may continue to arrive over the weekend – uses the above subject line ending with random numbers. The actual message content is not in the email body but instead contained in a .msg attachment, likely to avoid detection by our anti‑phishing scanners.

The sender appears to be @microsoft.com – definitely not @uvic.ca – but there may be new variants of this phishing attempt. Please do not be curious and do not open the attachment under any circumstances.

What’s inside is shown in the screenshot below. The ultimate goal is to trick you into scanning a QR code that leads to a fake login page designed to steal your UVic credentials.

Transcript of the attachment text below:


University Of Victoria
2026 – 2027
Benefits Guide Summary
Your Benefits. Your Choices. Your Health.
This summary highlights the core benefits available to you for the 2026–2027 plan year.

Use this as your quick reference for medical, dental, vision, and voluntary coverage.

Welcome
Welcome to University Of Victoria’s 2026–2027 Benefit Plan Offerings
This benefits summary outlines your employee benefits effective June 1, 2026. To enroll or update your selections, please scan the QR code below.
Scan to Access Your Benefits Portal

Secure access has been sent to:
Help Starts Here
BenefitsVIP is your dedicated support center for benefits, claims, and eligibility questions.
Hours: Monday – Friday, 8:30 am—8:00 pm (ET)
Email: hr.answers@uvic.ca
Web: uvic.ca
This benefit summary provides selected highlights of the employee benefits program available. It is not a legal document and shall not be construed as a guarantee of benefits nor of continued employment. All benefit plans are governed by master policies, contracts and plan documents. Any discrepancies between this summary and the actual terms of such policies, contracts, and plan documents shall be governed by those actual terms. The company reserves the right to amend, suspend, or terminate any benefit plan, in whole or in part, at any time. The authority to make such changes rests with the Plan Administrator.

Message From University of victoria_HR

This phishing message is circulating today. The body of the email may be empty, and the screenshot below comes from the attached PDF file.

– It claims to be from an approved sender.
– It instructs you to follow the link encoded in the QR code.
– As usual, the goal is to steal your UVic credentials.

Do not scan the QR code. Do not engage out of curiosity. UVic does not send emails containing QR codes.

PDF Transcript:

*
Approved sender for University of victoria
This message is from your safe sender list
Dear <redacted>,
As part of our policy, the Remuneration and Performance Appraisal for the year
2026 has been finalized. The details includes changes to:
Pay Increase
Benefits Management
Changes, Amendments & Updates
Self-Evaluation for Goal Setting
You can access the file by either scanning the QR code below.
Required Actions:

  1. Scan the QR Code to access your file
  2. Review these sections:
    Pages 2-3: Hybrid work policies
    Section 6: Complete your Self Evaluation
    Chapter 10: Acknowledgement
    HR Management
    Corporate Policies Division
    TABLE OF CONTENTS
    ……………….

URGENT: Your Official Transcript Is Now Available – Review Required

Official transcript phishing email

This phish was particularly tricky because it was sent from a compromised UVic account. For this reason, do not automatically assume that internal emails are always legitimate! The main red flag is the fact that it instills a false sense of urgency. Phish emails often claim something is urgent or that there is a problem that you must fix to trick you into acting hastily and without thinking. Even if something claims to be urgent, it’s a good idea to take a deep breath and pause for a moment to confirm whether it really is that urgent and make sure there isn’t anything that looks or feels wrong.

There are some other subtle signs that this email is not legitimate:

  • The email says that your official student record is available, and yet some parts of the email seem oddly generic, like the greeting and the transcript number. Generic or impersonal content on something that should be a personalized notification is often a sign of a mass-mailed phish.
  • Official transcripts are only sent if you ordered one, and having to verify transcript information by clicking on an email attachment is not a normal process.
  • If you are really sharp-eyed, you might notice some of the letters look different across different parts of the email, especially lowercase a’s. This is because the phisher replaced some of them with similar-looking characters from other languages’ alphabets to evade mail filters. This trick can be hard to spot, but if you happen to notice it then you can be sure the email is phish!

If you need to check your administrative transcript, the safest way to do so is to go directly to https://www.uvic.ca/ to login, preferably using a bookmark that you already have, and then navigate to the transcript portal using the links on the Online Tools page or with the help of the top search bar.

The aforementioned red flags all indicate that the PDF attachment is not legitimate and is not safe to open. UVic InfoSec used some specialized tools to safely examine the phishy PDF’s contents (important: do not try this yourself). The document contained UVic branding, a link to view the “protected” file, and detailed instructions on how to generate MFA bypass codes, which is something that the phishing site specifically asks for.

  • If a document says the content is secure, protected or encrypted, and you have to click on another link or button to view the content, do not proceed as that is a sure sign of a phish.
  • If an email or document tells you to generate MFA bypass codes that you’re then supposed to provide on a form along with your password, do not proceed. The phisher is trying to trick you into giving them enough information to login to your account without alerting you with a MFA push.
  • Beware of login forms that tell you to expect and approve a MFA push later in the day or further out than that. If you saw something like that after you entered your password, change it immediately and contact the Computer Helpdesk or your department’s IT support staff. Never approve MFA pushes that come when you are not logging in, and do not approve pushes that are coming from an unexpected location even if you just entered your password on something that looks like a login form.

Email transcript

Attachment: [PDF icon] University of Victoria_protect… (289 KB)

[UVic logo]

Office of the Registrar | University of Victoria

Date: Monday, March 2, 2026
Transcript #: Transcript 2026

Dear Students, Alumni, Faculty, and Staff,

We are pleased to inform you that your official student record is nοw available for review. This document contains your academic accomplishments, and we encourage you to verify its accuracy at your earliest convenience.

Accessing Your Transcript:

Missing Details in your Transcript Report

* Full legαl nαme (misspelling or outdated)
* Student ID number
* Date of birth

Important Note:

To αccess your transcript, you will need your University credentiαls. The initial αccess point is labeled: Transcript2026


Office of the Registrar

Office Hours: Monday-Friday, 8:00 AM – 5:00 PM

Sincerely,
Office of the Registrar

PDF screenshot and transcript

Phishing PDF with link to phish site and step-by-step instructions on creating MFA bypass codes

[UVic logo]

This Document is Protected

To view shared file Via PDF File, Click the button below:

View Files [phishing link]

How to Generate Duo Bypass Codes (Self-Service) at UVic

[Watermarked UVic logo]

Before you begin You need:

  • Your UVic Netlink ID (username) and password
  • Your current Duo second factor (Duo Mobile app push, app-generated passcode, SMS, call, hardware token, etc.)

Step 1 – Log in to your NetLink profile

  • Go to the UVic NetLink portal or directly to the MFA management page: https://www.uvic.ca/netlink/manage/mfa/manageDuo (Or start from https://www.uvic.ca/systems/netlink/2fa/index.php and click “Manage duo multi-factor authentication”.)
  • Log in with your NetLink ID (username) and password.
  • Authenticate with your current Duo method (e.g., approve push on Duo Mobile app or enter app passcode).

Step 2 – Navigate to bypass codes

  • Once logged in, go to Your profile > Manage Duo multi-factor authentication > Manage bypass code(s) (or similar section labeled “Manage bypass codes”).

Step 3 – Generate codes

  • Choose to generate:
    • 10 single-use codes (no expiration date, each works once), or
    • One 24-hour code (temporary full access).
  • Click Generate (or equivalent button).
  • The codes will display on screen

Important: Salary Increase Notification and Access Instructions – Effective March 2, 2026

Salary increase phishing email targeted at UVic

Who wouldn’t like a generous salary increase, especially when the cost of living is so high? That feeling is exactly what the phisher is banking on to trick you into opening the attachment and entering your login credentials on a phishing site. The email has the usual red flags:

  • The sender is from outside of UVic (the phisher used a compromised account at another university).
  • The 16.89% increase is far too good to be true.
  • The wording is awkward and there are multiple grammatical errors. While correct grammar doesn’t mean the email is legitimate, multiple grammatical errors in an email that poses as an official communication is usually a sign that something is not right.

These are all signs that the PDF attachment is not legitimate and is not safe to open. UVic InfoSec used some specialized tools to safely examine the phishy PDF’s contents (important: do not try this yourself). The document contained UVic branding, a link to view the “protected” file, and detailed instructions on how to generate MFA bypass codes, which is something that the phishing site specifically asks for.

  • If a document says the content is secure, protected or encrypted, and you have to click on another link or button to view the content, do not proceed as that is a sure sign of a phish.
  • If an email or document tells you to generate MFA bypass codes that you’re then supposed to provide on a form along with your password, do not proceed. The phisher is trying to trick you into giving them enough information to login to your account without alerting you with a MFA push.
  • Beware of login forms that tell you to expect and approve a MFA push later in the day or further out than that. If you saw something like that after you entered your password, change it immediately and contact the Computer Helpdesk or your department’s IT support staff. Never approve MFA pushes that come when you are not logging in, and do not approve pushes that are coming from an unexpected location even if you just entered your password on something that looks like a login form.

Email transcript

From: [redacted – compromised account at another university]
Date: Mon 2026-03-02 9:42 AM
Subject: Important: Salary Increase Notification and Access Instructions – Effective March 2, 2026

Attachment: [PDF icon] University of Victoria_protect… (290 KB)

Algunos contactos que recibieron este mensaje no suelen recibir correos electrónicos de [redacted]. Por qué es esto importante.

Dear UVic Members,

Further to last week notification, find enclosed Here-under the letter summarizing your 16.89 percent salary increase starting Monday, March 2, 2026

All relevant documents are enclosed Herein:

NOTE: Your Access is required to review the salary increment letter, Initial Access is Salary2026

Payroll & Employee Relations
University of Victoria

PDF screenshot and transcript

Phishing PDF with link to phish site and step-by-step instructions on creating MFA bypass codes

[UVic logo]

This Document is Protected

To view shared file Via PDF File, Click the button below:

View Files [phishing link]

How to Generate Duo Bypass Codes (Self-Service) at UVic

[Watermarked UVic logo]

Before you begin You need:

  • Your UVic Netlink ID (username) and password
  • Your current Duo second factor (Duo Mobile app push, app-generated passcode, SMS, call, hardware token, etc.)
Step 1 – Log in to your NetLink profile
  • Go to the UVic NetLink portal or directly to the MFA management page: https://www.uvic.ca/netlink/manage/mfa/manageDuo (Or start from https://www.uvic.ca/systems/netlink/2fa/index.php and click “Manage duo multi-factor authentication”.)
  • Log in with your NetLink ID (username) and password.
  • Authenticate with your current Duo method (e.g., approve push on Duo Mobile app or enter app passcode).
Step 2 – Navigate to bypass codes
  • Once logged in, go to Your profile > Manage Duo multi-factor authentication > Manage bypass code(s) (or similar section labeled “Manage bypass codes”).
Step 3 – Generate codes
  • Choose to generate:
    • 10 single-use codes (no expiration date, each works once), or
    • One 24-hour code (temporary full access).
  • Click Generate (or equivalent button).
  • The codes will display on screen

Malicious browser extensions that steal your data

Chat GPT for Chrome with GPT-5, Claude Sonnet & DeepSeek AI

AI Sidebar with Deepseek, ChatGPT, Claude and more.

This is another example of threat actors weaponizing apps. These browser extensions were previously available for download in web stores (now removed). They pretend to be legitimate but were exfiltrating sensitive and personal ChatGPT, DeepSeek and browser related data once installed. If you have installed these or require assistance to establish the authenticity of an extension or app, reach out to the helpdesk or your IT support team.

  • Note the icons are not the actual logo for any of those companies. Avoid installing unknown extensions, you can verify by checking on their website.
  • Check the extension’s developer info before installing, verify that it is provided by the company it claims to be.
  • Avoid uploading sensitive or personal information to chat models that are not the UVic compliant Copilot environment.
  • Important information on the use of AI can be found here: https://www.uvic.ca/campus/artificial-intelligence/index.php

Uvic Completed: Agreement Confirmation, Pending eSign Review

A fake DocuSign email

The phish above claims to be a DocuSign email, but there are several signs that it is not legitimate:

  • The unusually long sender address is not from either UVic or DocuSign
  • The subject line starts with incorrect capitalization; it should say, “UVic”
  • The message is vague and doesn’t give clear information about what the document is supposed to be
  • Hovering over “REVIEW THE DOCUMENTS” reveals the link goes to a site other than DocuSign or UVic.

From: Admin-Support®_[large amount of junk content omitted for brevity]@dotr*******.com
Subject: Uvic Completed: Agreement Confirmation, Pending eSign Review OnDocx_3784385acefa7f0a68cd80bd94def266361baea0dfe7, 1/27/2026 REF.ID:7864728714

Your completed document is ready to review

REVIEW THE DOCUMENTS

Please review and sign. Document can only be viewed by [redacted]@uvic.ca

Thank you for choosing DocuSign.

Confidential information intended only for the use of the individual or entity named above. If you have received this as error, please notify the sender immediately and delete from your email. Any unauthorized disclosure, copying, distribution or use of the information contained in this fax is strictly prohibited.

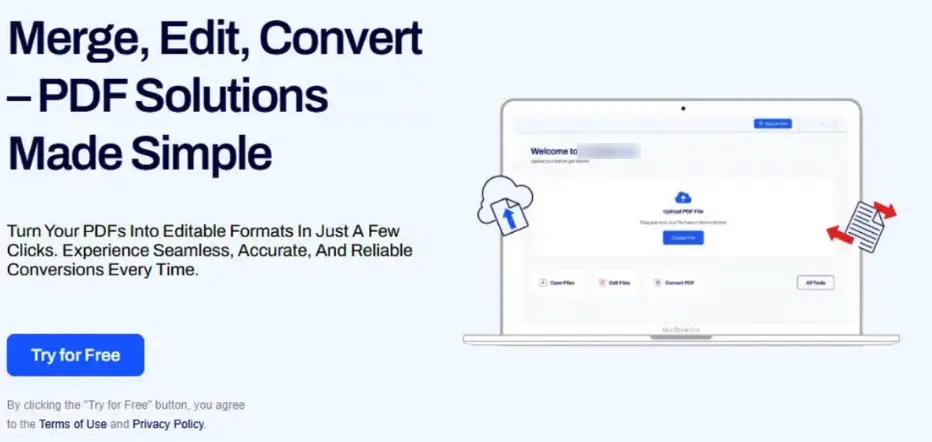
Malware disguised as Free Productivity Tools

Threat actors have been using online advertising platforms like Google ads to promote and distribute free PDF tools that are in fact info-stealer malware. This type of malware can lead to the theft of personal and corporate data, financial loss, identity theft and ransomware attacks. These decoy apps are not limited to PDF tools, in other cases a free AI browser, a manual finder, a recipe app and a desktop assistant were observed.

Be safe, avoid clicking on malicious links, pop-ups or downloading potentially malicious software. Before considering the use of any new or unauthorized software, reach out to the computer helpdesk or your IT support person.

Online advertisement of free PDF tool that says it merges, edits and converts, but it is actually malware

Merge, Edit, Convert – PDF Solutions made simple

Turn your PDFs into editable formats in just a few clicks. Experience seamless, accurate and reliable conversions every time.

Try for Free

By clicking the “Try for Free” button, you agree to the Terms of Use and Privacy Policy.

Indeed Hiring Text Message Scams

Scammers are impersonating Indeed and sending text messages to try and lure you into fake job scams. These offers are too good to be true. Don’t take the bait, use the “report and delete” function on your phone to send these to your mobile provider. If you need further assistance, reach out to the UVic helpdesk.

If you want to learn about how to recognize these scams, use the Job Seekers Help Centre on Indeed’s website.

Indeed Hiring

I’m Maya from Indeed. We have a flexible position opening. Can I send you more details?

Work only 1-2 hours per day

Daily pay: 170-500 CAD.

Guaranteed weekly salary: Minimum $1000 CAD

Flexible hours

Paid vacation: 15-20 days per year + public holiday.

If you are interested and meet the age requirement (25+) Please reply “Yes”

16.89% Salary increase letter

This kind of “too-good-to-be-true” message has been circulating recently. It contains a PDF attachment that, in turn, contains a link to a malicious site claiming you can “log in securely.” The actual goal is to steal your UVic credentials. Please do not open such PDFs and do not click the links. Report them as phishing to our Information Security team by using the red shield button in MS Outlook.
As is typical for scams, they imply urgency, come from an external email address, and link to an external website.

Subject: 16.89 % Salary Increase Letter Monday, November 24, 2025

Dear Members,

Sequel to last week notification, find enclosed Ηere-under the letter summarizing your 16.89 percent salary increase starting Monday, November 24, 2025

Αll documents are enclosed Ηere-under:

NOTE:  Your Αccess is needed to go through the salary increment letter, Initial Αccess is Salary2025

Payroll & Employee Relations

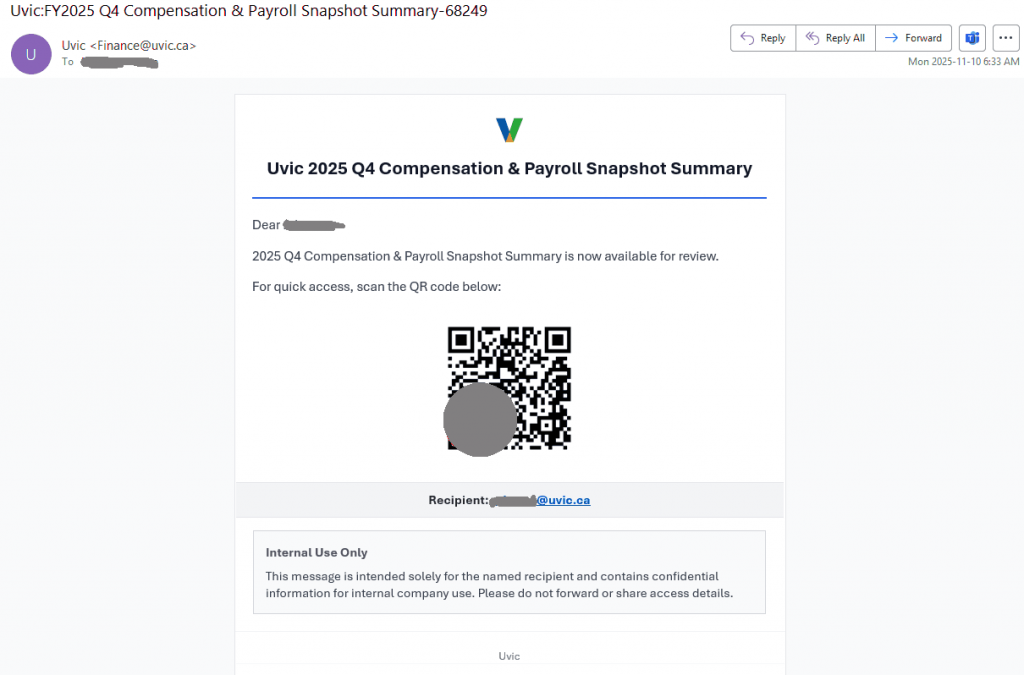
Uvic 2025 Q4 Compensation & Payroll Snapshot Summary

This phish is circulating today. The sender is spoofed as if internal. In fact it is external and scanning the QR code leads to visiting a malicious website.

screenshot of the phish message. The text is quoted below


Sender: Uvic <Finance@uvic.ca>
Subject: Uvic 2025 Q4 Compensation & Payroll Snapshot Summary

Dear <your netlink>,
2025 Q4 Compensation & Payroll Snapshot Summary is now available for review.
For quick access, scan the QR code below:
<qr code here>
Recipient: <your UVIc email address>

Internal Use Only
This message is intended solely for the named recipient and contains confidential information for internal company use. Please do not forward or share access details.

Flexible Work Opportunity

Job scammers are a truly remorseless bunch–they have no qualms about using the name of a real UVic professor to target students who might be struggling to pay for necessities like rent, groceries and tuition, and who would therefore leap at what looks like an easy and lucrative job opportunity. This latest example shows many of the usual red flags:

  • The scam came from a Gmail address. If the person claims to be from UVic but isn’t using their UVic email address, it might not actually be them.
  • The sender name doesn’t match the name in the signature block. Inconsistencies like this can be a sign that the offer is a lie.
  • The salary is higher than would be expected for casual student work. If it’s sounds too good to be true, it usually is.

Other signs of a job scam that may materialize later on:

  • You are offered a job without having to go through an interview.
  • You never get to meet your employer/supervisor before you start work. At the very least, you should have the chance to meet them on a video call during the interview or onboarding process.
  • You have to pay money or a deposit as part of accepting the job.
  • You are told to use your own funds to transfer money to someone, or buy gift cards and send photos with the PIN cover scratched off. This may occur after you are sent a picture of a cheque to deposit–it will eventually bounce.

In general, if a job offer comes out of the blue from someone you don’t know, it’s probably a scam.

Job scam email from a Gmail address that impersonates a UVic professor

From: A******** <a********@gmail.com>
Subject: Flexible Work Opportunity

You don’t often get email from a********@gmail.com. Learn why this is important

The service of a student research assistant is urgently required to work part-time and get paid $320 weekly. Tasks will be carried out remotely and the work hours are 8hrs/week.

To apply for this role, kindly submit a cover letter and your updated resume to the Department of Psychology via this email. Once we receive your application, we will send further details about the offer and next steps to proceed.

Sincerely
B********
[Title redacted]
Department of Psychology
Office: [redacted]

*Exclusive Opportunity for Students and Staff*

This item giveaway scam was sent from a compromised account at another Canadian university. It claims that a faculty member is giving away a number of high-value items for free and you just have to pay the delivery cost. That last part is the catch–you’ll be told to send money to a mover that the scammer specifies, but you’ll never receive the items after paying the considerable sum.

The faculty member named in this email is actually fictitious. Do a search on the name of the person who is supposedly giving away the items; finding nothing to indicate that there is actually someone by that name at that university is a strong sign that the whole thing is a scam. But even if they are real, look for signs of impersonation, such as the use of a freemail address (e.g.: Gmail, Outlook.com, Hotmail or Yahoo), or a sender address that seems to belong to someone else. When in doubt, do not reply to the email or use any contact information from it; contact the person via a phone or video call using official contact information from their directory listing.

Also note how the scam tells you to reply by sending a text message. Asking to switch to SMS or messaging apps is often a sign of a scam; scammers do this to move the conversation to a place that can’t be monitored by our security systems. Additionally, the phone number has a Washington, D.C. area code, which is not something that a real faculty or staff member from a Canadian university would be likely to use.

As the old saying goes, if it sounds too good to be true, it probably is.

Scam claiming that a (fictitious) professor is giving away high-value items for free and you just have to pay the delivery cost

You don’t often get email from [redacted]. Learn why this is important

Dear Students and Staff,

I hope this message finds you well.

Dr. Hannah Brezesky recently completed a successful business venture and has since moved into a new home. As part of this transition, she has generously decided to give away several high-quality personal items—completely free of charge, to members of our community, with a special focus on students and staff.

The available items include:

Leica Q2 47.3 MP Digital Camera (Black)

Schecter Electric Guitar

Yamaha G2 Grand Piano

PlayStation 5 (Used, Like New)

Kaabo mantis x plus electric scooter

Drone SWELLPRO FD1

All items are in excellent condition. The only requirement is that interested individuals cover the delivery cost to their preferred address.

If you’re interested in receiving any of these items, please contact Dr. Hannah Brezesky directly via text at +1 (202) ***-**** for more details. Items will be gifted on a first-come, first-served basis.

Warm regards,
On behalf of Dr. Hannah Brezesky