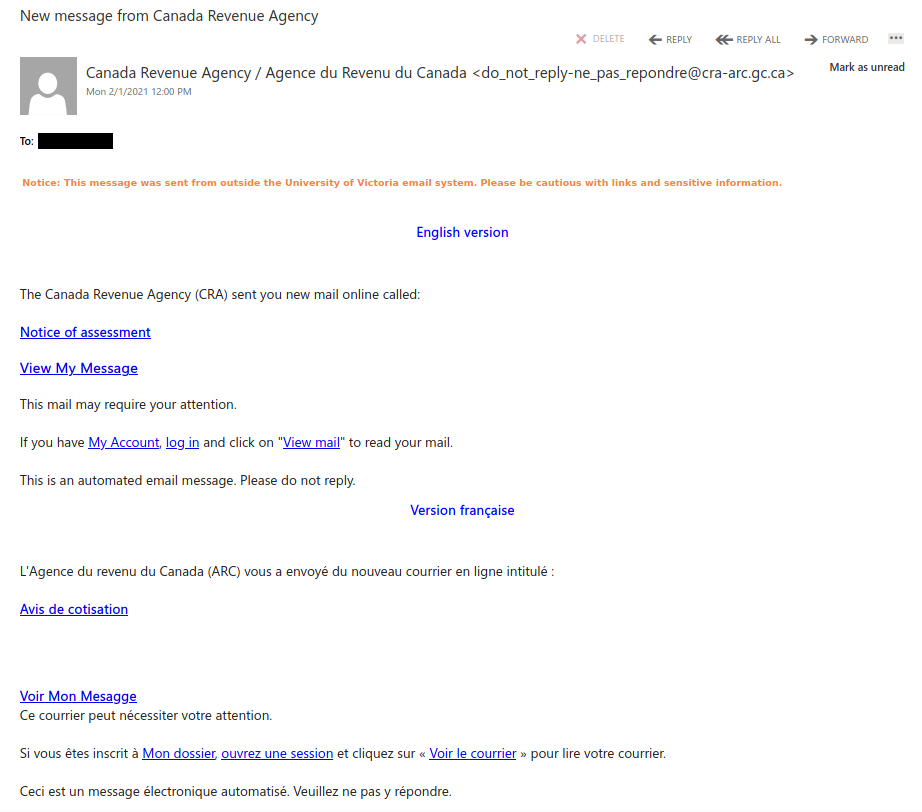
New message from Canada Revenue Agency

This phish may look like it came from the CRA, but don’t trust that sender information–in this email, it is spoofed!

If you were to hover over any of the links, you would see that it although they contain “cra-grc”, the site is not canada.ca or cra-arc.gc.ca, so it is dangerous to click on those links. The destination is actually a very realistic copy of the CRA login page designed to steal your login credentials.

The CRA has some tips on how to recognize scams here: https://www.canada.ca/en/revenue-agency/corporate/security/protect-yourself-against-fraud.html

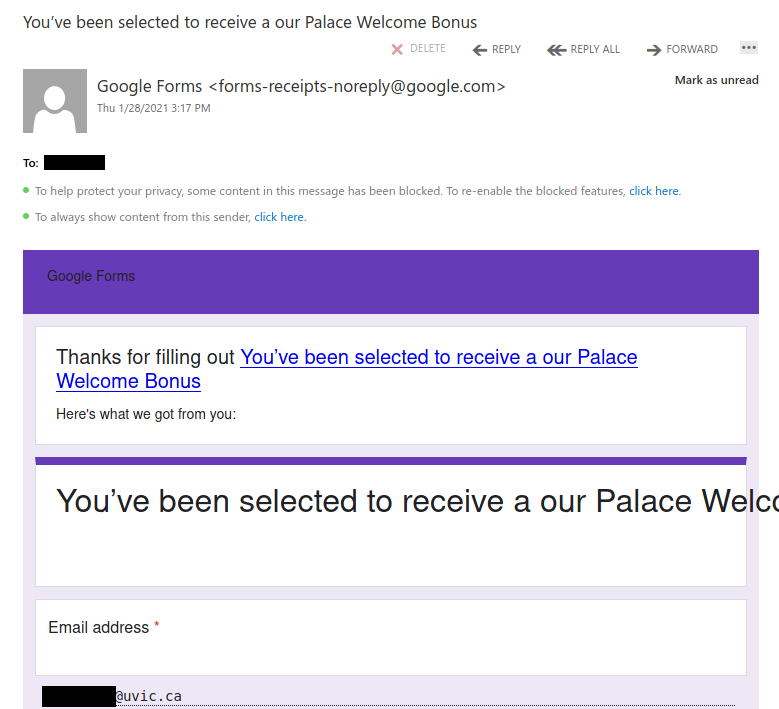
Phish sent through Google Forms submission receipts

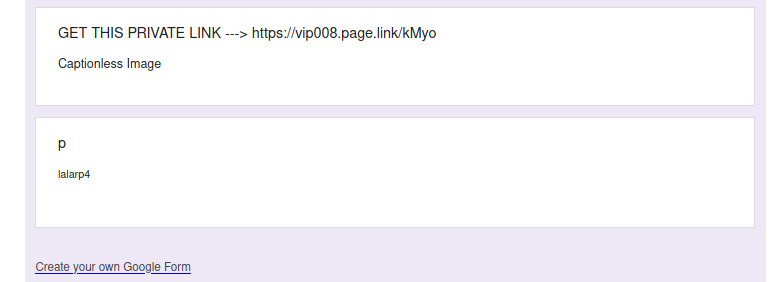
What appears to be happening here is a phisher created a Google Form and then made a bogus submission where they entered someone else’s email address. The result: that other person is emailed a genuine Google Forms submission receipt  but the content of that email is actually phish.

Phishers often abuse legitimate services like Google Docs or Forms to send and/or host phishy content. If you receive an email notification from a service like that, think about whether it’s related to an action you remember doing or if it’s something you were expecting from someone you know. If not, it’s probably phish, so don’t click on any links.

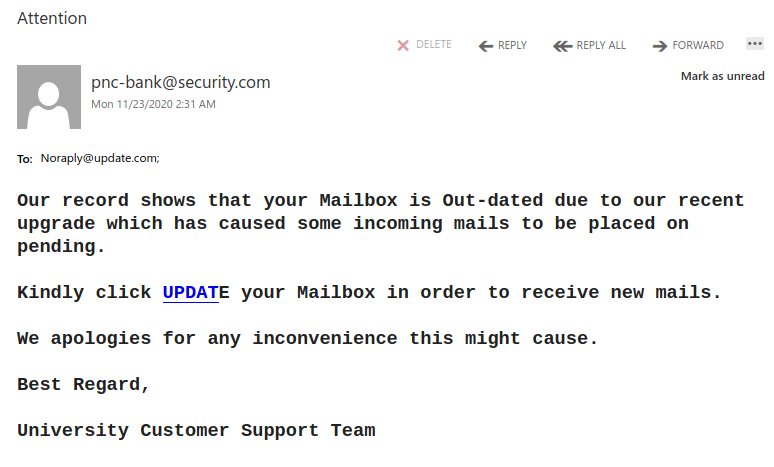
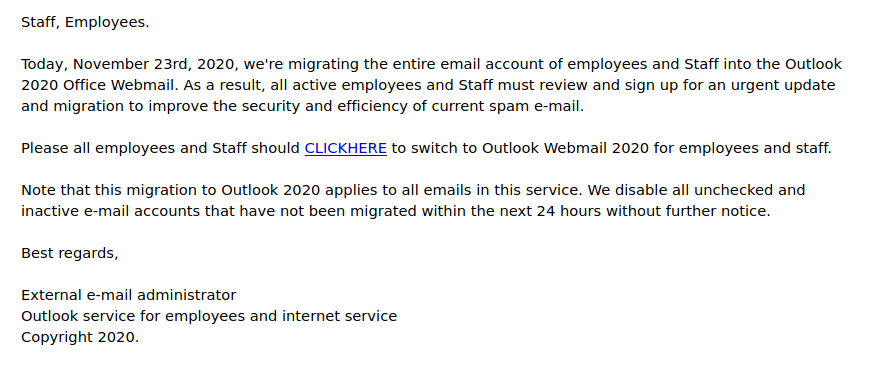
“Mailbox Quota Warning” phish

Another phish was received by a number of UVic recipients today. It uses the usual tactics – to scary the recipient that something is wrong and the victim needs to fix it. In this case the subject is “UVic Mailbox Quota Warning” and the email claims several messages were pending because the mailbox was full. (see the screenshot below). When the victim clicks on the link a fake Outlook Web Access (OWA) page opens. All designed to steal your UVic credentials.
As we always remind you – please do not be curious and do not click on such links – they may contain other malicious content so that just opening them “for a quick glimpse”  may be dangerous.
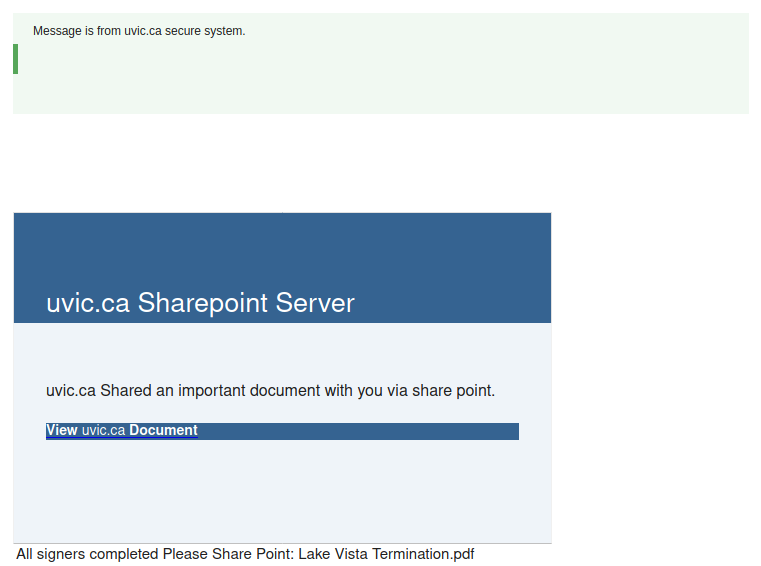
Note that they added their own message (the green bar) to fool you that the email originated from UVic.

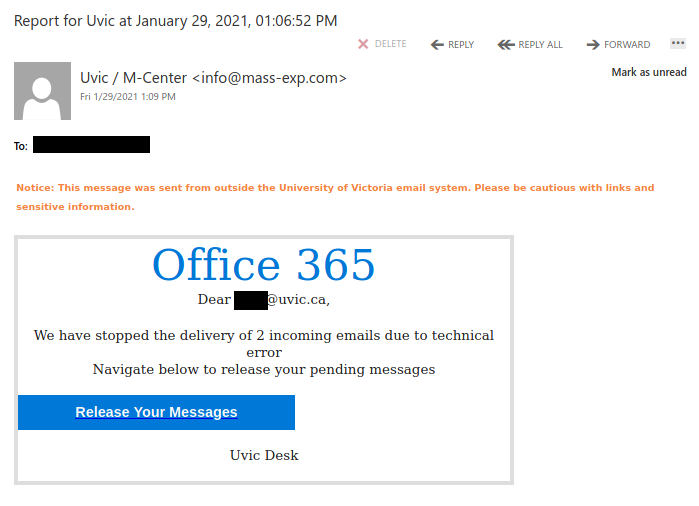
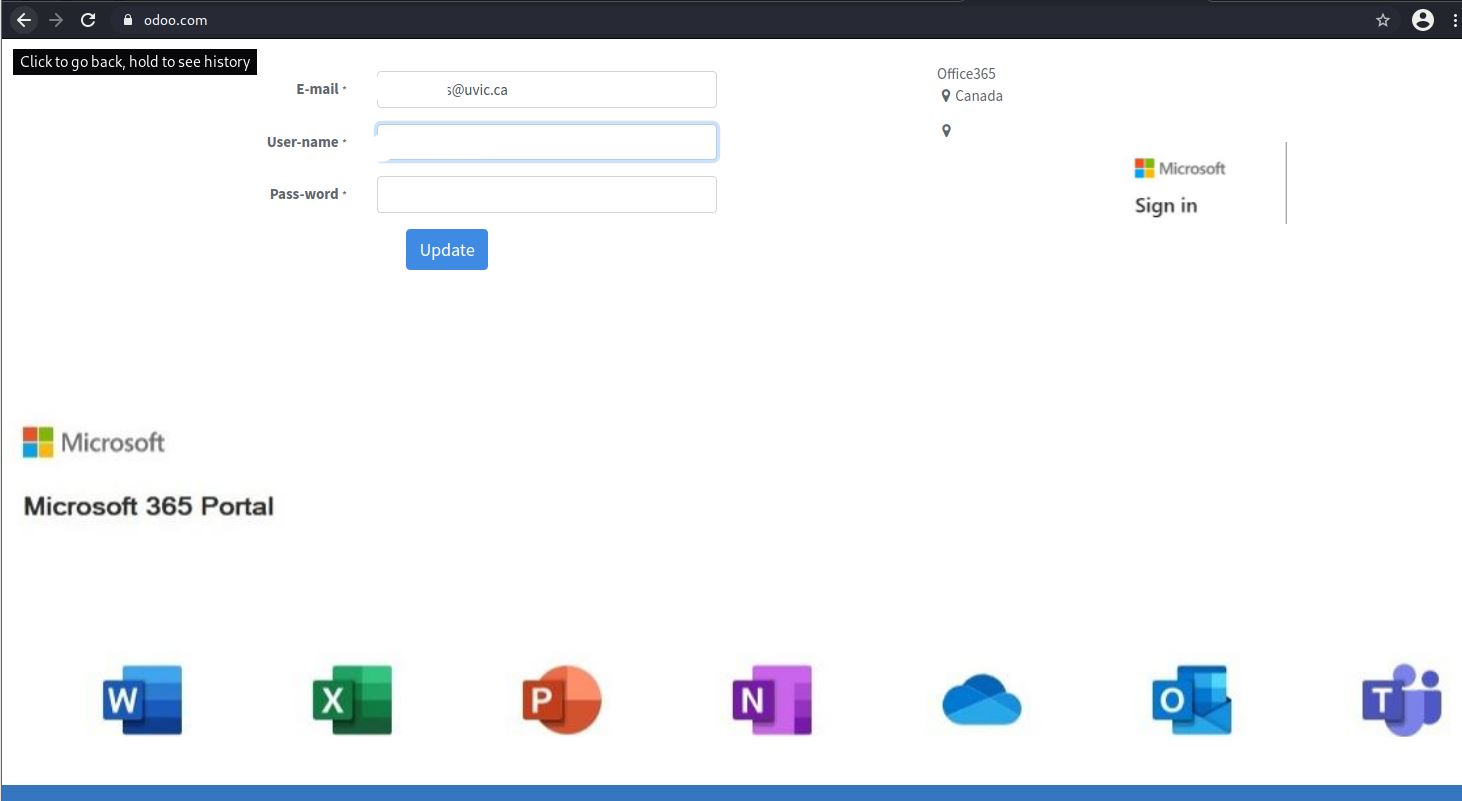
Fake M365 Logon page

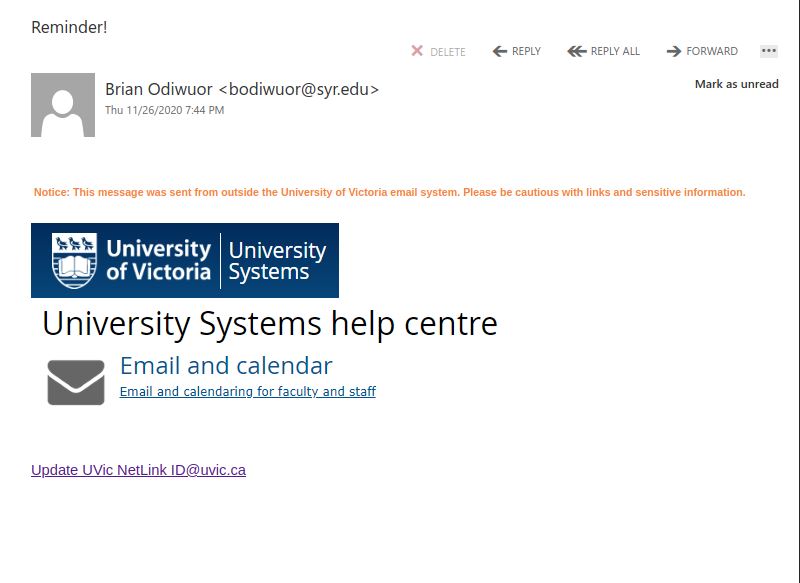
Phishing email using our University of Victoria Logo. Note the sender email and the external email banner.

M365 Email

Visiting link will bring you to Fake M365 logon page which has nothing to do with UVic:

With the overall increased usage of M365 by many, it is important to be careful as criminals will attempt to deceive you with the “newness” of various products.

Check for valid senders and review the Internet Address/URL closely.

Whenever in doubt, go directly to known good logon windows and refrain from using links in email.


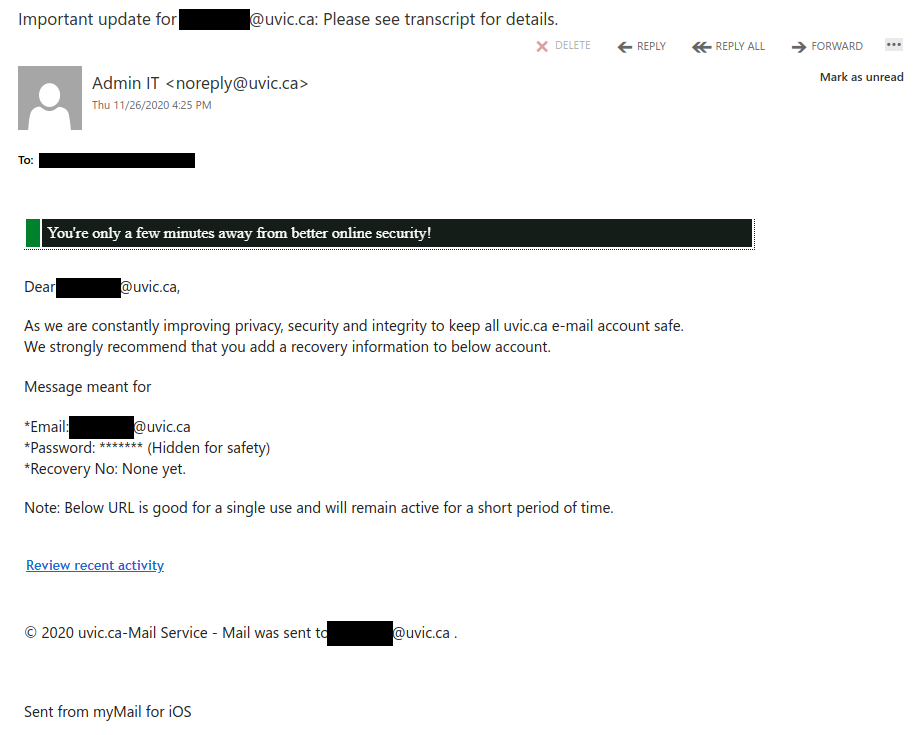
A fake call to improve privacy and security

This phish with a spoofed UVic sender address tries to convince you that you need to click on the link to help improve your privacy and security. But hovering over that link shows that it actually leads to a non-UVic site, so of course, clicking it would achieve the opposite outcome.

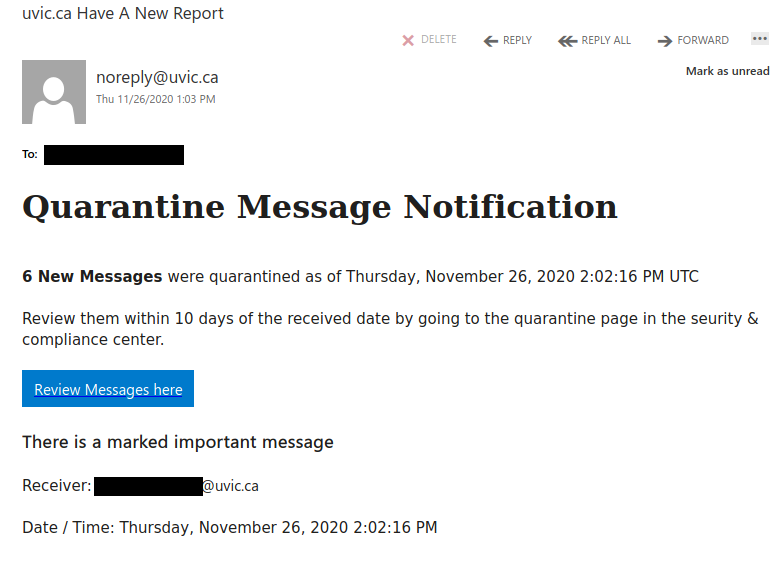
uvic.ca Have a New Report

While this message claims to be from noreply@uvic.ca, that is fraudulent (spoofed sender again). This phish also uses individualized click-tracking links, so don’t click on them–the phisher is probably watching to see who clicked.

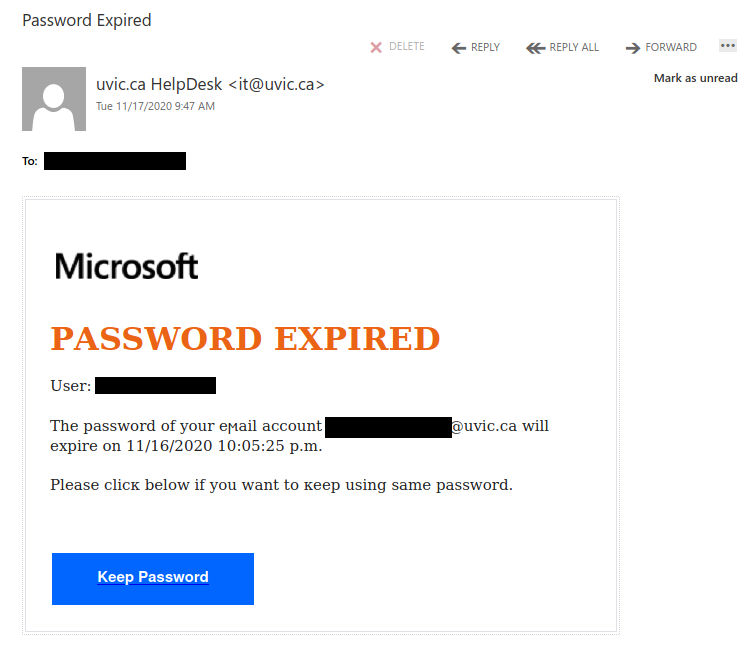
Password Expired

This phish also spoofs a UVic sender address, but also did not come from UVic and actually goes to a fake OWA login page. Remember that the real Computer Help Desk will never send you an unsolicited email telling you to click on a link to do something about your password.

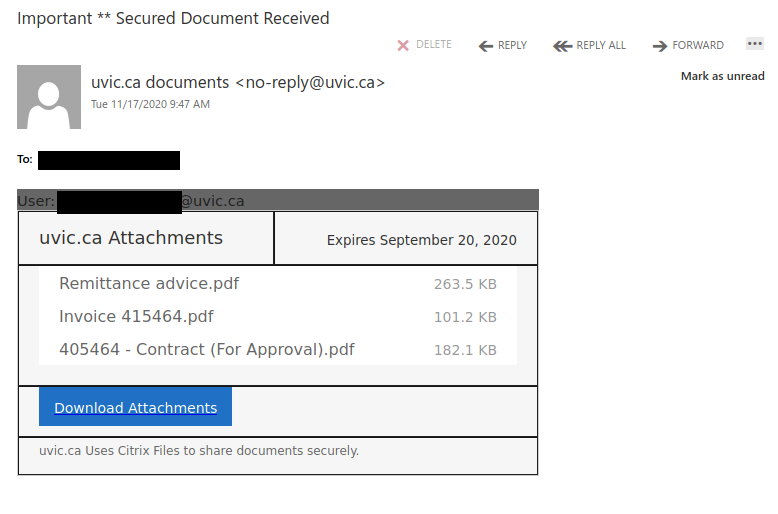
Important Secured Document Received

This is yet another spear phish that spoofs a UVic sender but did not come from UVic. It actually goes to a fake OWA login page.

Remember: treat any files that are not from UVic-managed file sharing services with caution, especially if you were not expecting them.

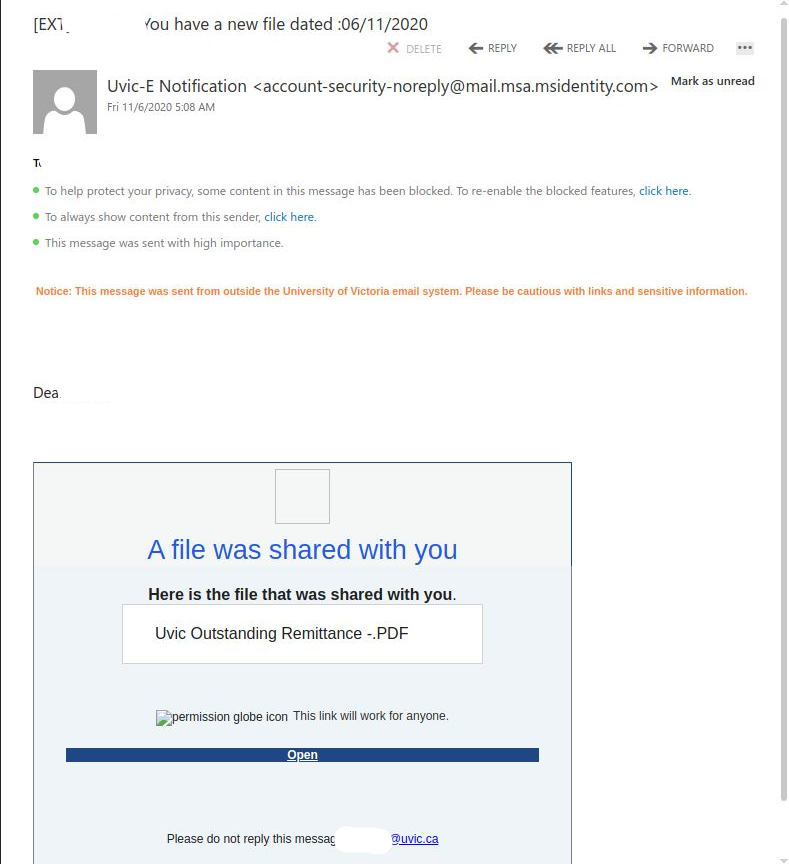
You have a new file dated: 06 /11/2020 from UVic-E Notification

This one emphasizes the need to consider where you are accessing files from and how you expect them to be shared with you. UVic managed services are the only recommended way to share UVic work related documents.

This one is tricky. You cannot rely on the visible senders here so much and of course there is some comfort in seeing they are using your legitimate name and email address. The supposed download also has Uvic in the name. NOT LEGIT.

The caution here is, now that many of  us are working from home and with the growth of cloud service use, specifically Microsoft and other big name products, we are becoming more comfortable with the idea that we may receive something legit from those sources. If you look at the body of this message, it does look phishy but it also looks as if it is coming from a known good Microsoft domain.
MSID

What you don’t see is a bad sender used/abused the Microsoft service to add a bit of authenticity to the message. This one was actually sent from a likely compromised .jp email address.

Question to ask yourself:

  • Which services are UVic managed and offer sharing among your teams? How have you been sharing with your department all along? In most cases, they are accessible outside the email link reference and directly accessible via your UVic device or an application you use regularly.

PAUSE.

Follow your gut.

There is no rush.

This one doesn’t include a known contact but oftentimes, you can call your colleague or contact them via a different known good method. eg. phone, and verify whether or not they have sent you something.

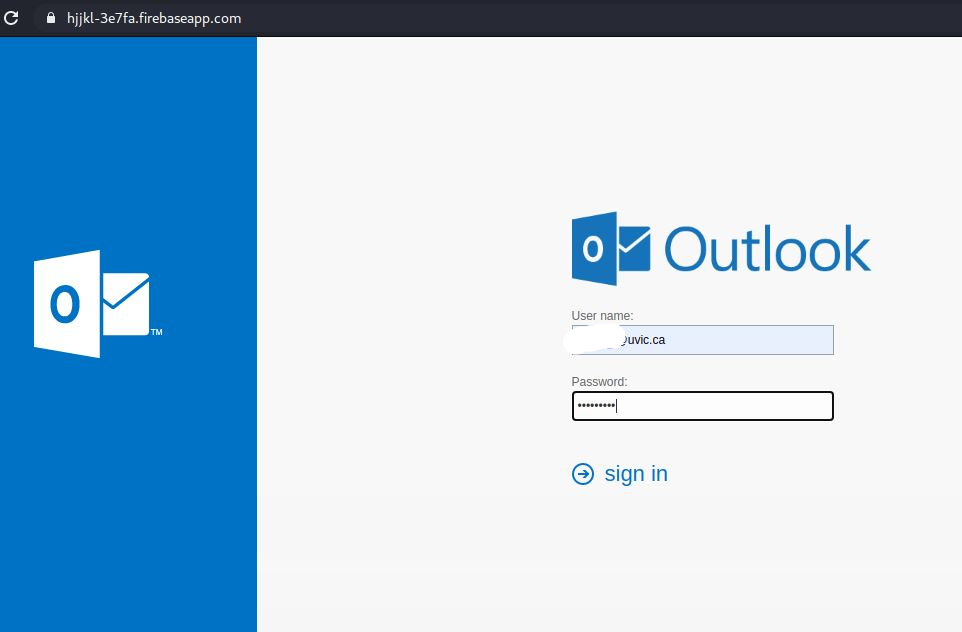
In addition to Microsoft service being abused here, if you hold your mouse over the PDF or the Open link, you’ll see they are also abusing a legit Google hosting service called firebase. The Firebaseapp is the legitimate Google service, the trailing link off the end goes to a website, that again, is NOT LEGIT.

If you proceed to view the PDF or click on the Open Link you will land on a fake Outlook Web App page that you are used to seeing. Yes, it does not have the UVic logo in this case, but we often see that level of duplication. The key in this case again is to look at the Internet Address.

In my sample, I am not revealing the email address but these are also customized with your personal work email in the URL and already populated in the User name text box. If you provide your legitimate password, they will capture it for later use and then conveniently, will just sent you back to the main UVic logon page.
Fake OWA